Cyrisma Updates - What to Expect
Last updated: September 24, 2026
Cyrisma has just received its largest platform update to date.
This release introduces a new endpoint agent, a new vulnerability engine, significantly expanded patching capabilities, centralized MSP operations, and new ways to prioritize vulnerabilities across your client base.
2026/09/23 10:40AM EST
Agent Rollout Update
The new Cyrisma agent is now available to all customers, and the large majority of devices in the field have already upgraded automatically. Upgraded devices are reporting normally and are being actively monitored for vulnerabilities and configuration posture.
Need a Hand?
If anything still looks incomplete after that, or if you have any questions at all, please contact support@cyrisma.com or open a ticket here. We'll be glad to take a look with you.
Immediate Considerations
The MSP and Tenant dashboards will show zero counts for certain tables and graphics until agents upgrade, which is expected to occur throughout the day.
As agents update, the MSP dashboard may initially lag behind the Tenant dashboard in what data is shown.
All historical data is preserved, but may not show in the dashboard.
Certain Mac and Linux environments may require reinstall. If any action is required - the Cyrisma team will reach out directly.
Vulnerability and configuration findings may change slightly as we have added 10+ new threat feeds while updating CIS benchmark controls.
For EDR whitelisting, the Cyrisma file folder location has changed.
Previous: C:\CYRISMA_Agent
New Location: C:\Program Files\CyrismaAgent
For more details on EDR check: Whitelisting the Cyrisma Agent in Common Endpoint Protection Platforms | Cyrisma Knowledge Base
Previous: C:\CYRISMA_Agent
New Location: C:\Program Files\CyrismaAgent
Logs are now located at C:\ProgramData\CyrismaAgent
Legacy Assets and Endpoints
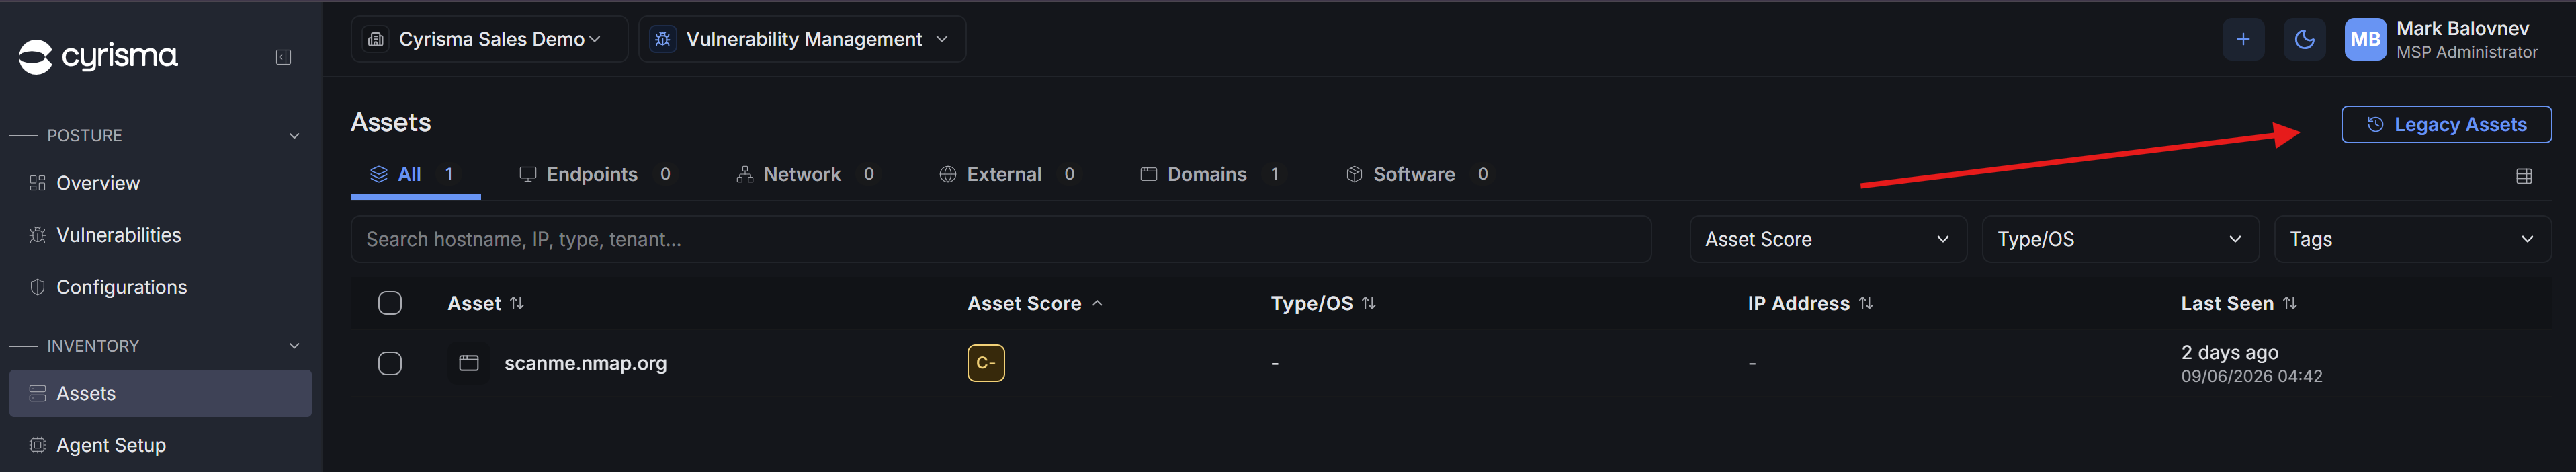
The MSP dashboard will only show agents that have upgraded to the latest version
Tenant/Instance views have a "Legacy Assets" button in the top right to view agents that have not yet upgraded.
Summary of Updates
Scanless monitoring model - vulnerability and configuration detection becomes near-real-time
Expanded threat intelligence improves root-cause accuracy, prioritization, and false-positive reduction
Scanning, patching, and reporting are centralized for global automations
Automated patching support for 10,000+ third-party patches
Maximum agent memory usage reduced to <90MB
SSO, global tagging & suppression management, and more features are bundled in.
What Happens Next?
This release represents the beginning of a broader shift in Cyrisma from traditional vulnerability management toward vulnerability operations — continuously identifying, prioritizing, and ultimately remediating vulnerabilities with less manual intervention.
We'll continue releasing additional functionality and documentation as the rollout progresses.
If you run into any issues, please contact support@cyrisma.com or open a ticket here.